Our views on technology, security, marketing & design
AllAICloud BackupCloud SecurityConsumer ProtectionCritical InfrastructureCybersecurityData BreachData ProtectionDigital MarketingEmployee TrainingEthicsIT SecurityLocal BusinessLocal NewsMacNewsPrivacyScamsSelf-HostingShared HostingSmall BusinessSmart HomeTechnologyTips & TricksUncategorizedWeb Design
A business owner called me because her website felt slow and wasn’t bringing her calls. Within a few minutes I was looking at her invoices — sitting in online storage with no password on it. And they weren’t the only thing there. Signed contracts. Tax documents. Scans of identification. Then I realized not all of it was hers: the person who built her site had been using the same storage for EVERY client and never turned the lock. She had no idea — of course she didn’t. She hired someone to build a website. She was never going to know to ask, and nobody told her. That call isn’t unusual anymore. Here’s what I keep finding when I get called in: the security problems nobody can see, the ‘handcrafted’ claims that aren’t true, the sites that don’t work while charging premium rates — plus why your website is the first conversation you have with almost every customer you’ll ever get, what it actually means to own the whole thing instead of one piece, and the fourteen questions every business owner should ask before hiring anyone. This isn’t an anti-AI article. I use AI every day. It’s about what happens when a powerful tool lands in unaccountable hands.
If you have a Florida driver’s license — or family who does — you’ve seen the headlines: a hacking group says it broke into the state’s driver database, stole 200,000+ records, and will publish them September 11 unless the state pays. As proof, it posted a full driver record, Social Security number and all. It’s the third major identity-document story in barely a week. Here’s what we’re doing with it: separating what’s CONFIRMED from what’s merely CLAIMED (the gap is wide — the state and FBI haven’t responded, and an independent outlet couldn’t verify the sample); explaining what the system actually is (it’s NOT the website you renew tags on — it’s the restricted law-enforcement database, and nobody opted in); a short practical list for Floridians and everyone else (the group says other states are next); and the two lessons for every business — because the attackers say they got in through a PASSWORD-RESET flaw, a side door your business almost certainly has.
For months, officials warned it was coming — and now it appears to have happened: a cyberattack knocked a small British power generator offline for four days this summer, on the heels of attacks that struck 30+ community water systems in the US. British security officials attribute the power-plant incident to hackers linked to Iran; US authorities connected the water attacks to the same source. Here’s the thread that ties them together: the targets weren’t massive national grids. They were SMALL. A generator a UK minister called ‘tiny.’ Community water systems. These attacks succeeded not by overpowering the strongest defenses but by finding the weakest — the small, under-resourced, lightly-defended facilities everyone assumed were too minor to bother with. If that sounds like most small businesses, it should. Being small isn’t camouflage — it’s what put these facilities in the crosshairs. Here’s why, and the achievable steps that turn you from a soft target into one attackers skip past.
The headlines this week grabbed everyone: US officials announced a state-sponsored hacking operation linked to China had targeted NASA, the Federal Reserve, the US Senate, the Department of Justice, and other agencies. It sounds like a spy thriller — but buried in it is a detail that matters enormously to ordinary small businesses, and it has nothing to do with being a government agency. The attackers didn’t launch from their own computers. They hijacked THOUSANDS of everyday internet-connected devices — ordinary routers and network gear belonging to regular people and businesses — and used them as disposable stepping stones to carry out and disguise their attacks. The equipment used to go after NASA may well have included hacked devices sitting in small offices that had no idea. To a global attacker, your under-secured router isn’t valuable for its data — it’s valuable as a weapon. Here’s why ‘we’re too small to be targeted’ misses the point entirely, and the ordinary fixes that keep your equipment from being conscripted.
The backpacks are packed and a new school year starts tomorrow — so here’s a thought to go with it: your business website is a lot like a student. And most small-business websites are the kind that aced one test years ago and have been coasting on that grade ever since, quietly falling behind while the rest of the class keeps moving. A website that was BUILT ONCE is very different from one that KEEPS SHOWING UP to learn. In honor of the first day of school, here’s what it means to have a website that behaves like a straight-A student instead of a forgotten one: it shows up every day (we don’t disappear after launch), it does its own real work (no AI slop — hand-built by a real engineer), it keeps learning all year (we continuously improve it), and it brings home results (leads and booked clients). Plus a quick report card you can run on your own website today.
Here’s a story that should permanently retire the most dangerous idea in small business security: ‘we’re too small to be a target.’ A company whose components sit inside Patriot and THAAD missile-defense systems, fighter jets, satellites, and torpedoes was just breached — not by a foreign intelligence service defeating military-grade defenses, but because ONE employee clicked ONE link. A fake ‘shared document’ from a supposed business contact, a counterfeit Microsoft login page, one password typed in, and an attacker was inside the mailbox of a company that arms the US military. We know the details precisely because they were disclosed in an SEC filing. The exact technique used here is the identical one aimed at accounting firms, medical practices, and contractors every day — and here’s what it means for you, including the one habit that would have stopped it cold.
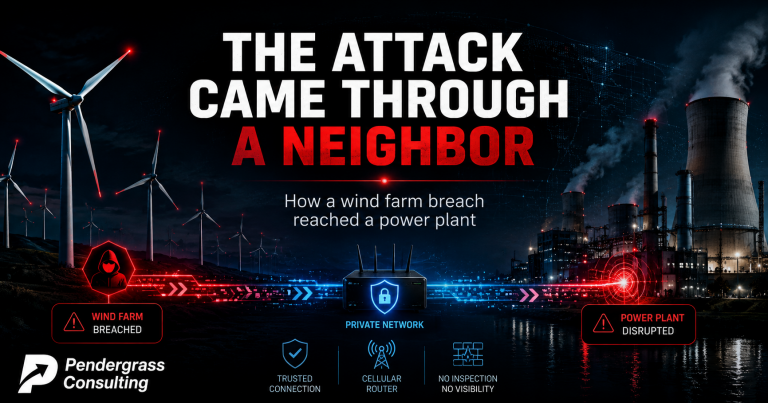
Early on December 29, a steam turbine at a Polish power plant serving 50,000 people stopped — along with the system treating its water. When investigators spent three months piecing it together, they found something never documented before in a real attack. The hackers didn’t break into the plant directly. They broke into a separate WIND FARM miles away, then walked from one to the other through a shared network that NEITHER facility controlled. It’s the first known case of attackers reaching industrial controls this way — and the lesson isn’t about power plants. It’s about the trusted connections hiding in every business: the vendor with remote access, the managed device in the closet, the link between your two locations. Your security is only as strong as the things you’re connected to — including the ones you don’t control and can’t see.
There’s a comforting belief a lot of business owners hold: ‘if my files ever get locked up, I’ll just restore from backup and tell them to get lost.’ It’s a good instinct — and it’s exactly the plan a ransomware operation called Gunra is built to defeat. Gunra doesn’t just lock your files. It steals a copy first, then goes hunting for your backups to destroy them. When your safety net is gone, ‘I’ll just restore’ stops being an option. It’s serious enough that CISA, the FBI, and South Korean authorities issued a joint advisory. Here’s how it gets in (through unpatched firewalls and VPNs — a door you can close), the three-part squeeze it puts on victims, and the backup and patching habits that actually defeat it. Every part of its playbook has a specific, achievable counter.