The headline going around today says researchers used one AI company’s model to hack another AI company in under 72 hours. That’s accurate. But three things the headline leaves out change what the story actually means — and the most useful one has nothing to do with artificial intelligence at all.
Let’s start with the correction that matters most, because a lot of the coverage reads like a heist.
First: this was authorized, and it worked the way it’s supposed to
Nobody committed a crime here. A small security firm, Hacktron AI, was participating in OpenAI’s official bug bounty program — the arrangement where a company invites researchers to find holes in its systems and pays them for reporting them privately.
The researchers found a chain of flaws, proved they could reach OpenAI’s private source code by opening a harmless pull request, and stopped there. They reported it through the bug bounty platform on July 25. OpenAI patched the vulnerabilities within 14 hours and paid a $6,500 bounty. The full cost to the researchers was under $3,000 in AI usage.
So the correct reading of this story isn’t “an AI company got breached.” It’s “a company’s security program found a serious problem, fixed it the same day, and paid the people who found it.” That’s the system working. We’re stressing this because the difference between authorized research and an attack is the entire difference between a good day and a catastrophe, and the headlines flatten it.
One more bit of housekeeping before the substance: we use AI tools every day in our own work, and we’ve written before about why the tool isn’t the problem. This article isn’t a case against AI, and it isn’t a scoreboard between AI companies. Which model was involved is genuinely the least interesting fact in the story.
What actually happened
Here’s the chain, in plain terms. Follow the shape of it, because the shape is the lesson:
- They started at the community forum. Not a core system — the public discussion forum, which runs on widely-used off-the-shelf forum software.
- They found a flaw in how it handled image uploads. A particular image format wasn’t supported by the forum’s normal image inspector, so those files got routed to a different conversion tool, which passed them to an underlying image-parsing library. That library had a memory-handling bug, and a specially crafted image could exploit it to run code on the forum server.
- They used that to take over a user account. The way logins were handled between the forum and the company’s main sign-on system allowed an attacker with control of the forum to take over accounts of people who visited it — including employees.
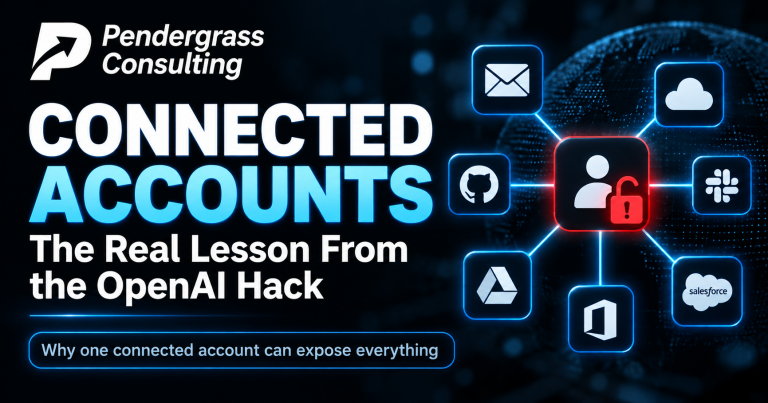
- The account was connected to everything else. One compromised employee account had a coding assistant linked to the company’s source-code repository. Through that connection, the researchers reached the private code. Reporting indicates other connected services — email and chat among them — were reachable too.
That’s it. A forum, an image library, a login flow, and a connected account. Now let’s take the three lessons in order of how much they should change what you do on Monday.
Lesson one: the vulnerabilities were completely ordinary
Read that chain again and notice what’s not in it. There’s no novel attack technique. No AI-specific vulnerability. Nothing that didn’t exist as a category twenty years ago. A bug in an image-handling library, a weakness in how single sign-on was implemented, and an over-connected account. These are the bread and butter of security work, and every one of them has been written about in textbooks.
This is the same observation we made about the flaws a researcher found in NASA’s spacecraft-commanding software: the target was extraordinary, the mistakes were ordinary. It keeps being true because it’s how security actually fails. Nobody needs a new class of weakness when the old ones are still lying around.
So the takeaway is not “AI created a new threat.” It’s that AI dramatically compressed the time needed to weaponize weaknesses that were already there. The holes didn’t change. The effort required to find them, chain them together, and build a working exploit did — from something that takes a skilled specialist weeks, to something that takes a small team a weekend. If your defense strategy has ever quietly relied on “that would be too much work for anyone to bother with,” that assumption is the thing this story breaks.
Lesson two: the capability line moved, visibly, in weeks
Here’s the detail the researchers themselves highlighted, and it’s worth reporting precisely because it’s uncomfortable rather than because it’s exciting.
They first tried to build the exploit with the AI model generation available at the time. It failed — reportedly struggling across several sessions without producing anything that worked. Then a newer model version was released. Same team, same task, and the agent produced a working exploit in a matter of hours.
We want to be careful about what to draw from that. It is one data point, from one team, on one task, and the researchers had a specific, capable setup — reporting indicates they had access to a version made available to vetted cybersecurity practitioners rather than whatever a member of the public can sign up for. That gating matters and deserves mentioning. It’s also not permanent: capability that’s restricted today tends to be widely available later, and there are already less-restricted models in circulation.
With those caveats, the trend line is hard to ignore, and it’s the same one we’ve been tracking all year from completely unrelated directions: a device-takeover exploit built in under a day with fewer than 20 prompts, supposedly tamper-proof forensic files altered in 45 minutes, and now a chain into a major company’s source code over a weekend. Different researchers, different targets, same direction. Whatever “too hard to be worth it” meant last year, it means less this year.
Lesson three: one account was connected to everything
Now the part that should actually change something in your business this week, because it’s the link in the chain you can do something about.
The researchers didn’t go from “we control a discussion forum” to “we’re reading private source code” through some brilliant leap. They got there because one employee’s account was connected to a coding assistant, which was connected to the company’s code repository. Each connection was made for a good reason. Each one saved somebody time. Together they formed an unbroken path from a public forum to the crown jewels.
Your business has this exact structure, and it’s grown without anyone deciding to build it:
- “Sign in with Google” or “Sign in with Microsoft” on a dozen services. Convenient — and it means one compromised email account unlocks all dozen.
- Apps you’ve granted access to your email, calendar, or files. Scheduling tools, CRM integrations, e-signature services, that AI assistant somebody connected in March. Each one holds a standing key to your data, and almost nobody revisits the list.
- Your accounting software linked to your bank. Your point-of-sale linked to your accounting. Your website linked to your payment processor.
- Password managers, browser sign-ins, and saved sessions that turn one device into a key ring.
The question to ask isn’t “is my email secure?” It’s: if someone got into my email account tonight, what else would they be holding? For most small businesses the honest answer is nearly everything, because the email account is the hub every other connection was built around. That’s the same lesson we drew when a stolen credential from a partner agency opened a state driver database, and when criminals used a compromised government mailbox to talk a bank out of customer files — the account is never just the account. It’s everything the account can reach.
Worth asking about your own business: When did anyone last review which third-party apps have standing access to your email, files, and calendar — and remove the ones nobody uses anymore? * If your main email account were compromised tonight, what else would that unlock? * Does any single employee account have a path to your most sensitive data, and does it need one? * And who is responsible for updating the third-party software your business runs but didn’t write?
The other half of the story: it cuts both ways
It would be easy to end on alarm, and that would be both lazy and inaccurate. Look at what else this story demonstrates.
The same capability that let a three-person team chain four flaws over a weekend is available to the people defending systems. Finding vulnerabilities before criminals do is exactly the work that just got dramatically cheaper and faster. A bug bounty program — a defensive investment — is what surfaced this, and it surfaced it because the company had made it worth someone’s while to look and report rather than exploit. The fix landed in 14 hours.
That’s the actual arms race, and defenders are not on the losing side of it by default. But it does raise the floor. When finding and exploiting weaknesses gets cheaper for everyone, the businesses that get hurt are the ones whose weaknesses were never going to require much effort in the first place — the unpatched third-party software, the forgotten integration, the account connected to everything, the thing nobody owns. Those have always been the problem. They’re just going to be found faster now.
What to actually do
None of this requires you to have an opinion about AI:
- Audit your connected apps and remove what you don’t use. In your email and file platforms there’s a list of third-party applications with standing access. Go look at it — most owners are startled by what’s on there. Revoke anything nobody can account for, and make this a twice-a-year habit.
- Map your blast radius. Write down what your main email account unlocks. If the list is “everything,” that’s the risk to work on first, and it usually starts with strong multi-factor authentication on that account specifically.
- Patch the software you didn’t write. The entry point here was ordinary forum software with an out-of-date component underneath it. Your version is the website plugin, the camera recorder’s firmware, the tool a vendor installed. Somebody needs to own keeping it current, and in most small businesses nobody does.
- Limit what integrations can reach. When you connect a tool, give it access to what it needs rather than everything. Most platforms allow this and almost nobody uses it.
- Stop relying on obscurity and effort. “Who’d bother with us” was always a weak defense. It’s weaker now.
The takeaway
Strip away the two famous names and this is a very familiar story. A public-facing system running third-party software had an unpatched component. A login flow trusted something it shouldn’t have. An account was connected to more than it needed to be. Somebody with modern tools walked the chain in a weekend, and because they were authorized and honest, the company fixed it in 14 hours and paid them for the trouble.
The AI angle is real and worth watching, but it’s the amplifier, not the cause. The cause is the same thing it always is: a path that existed, made of ordinary mistakes, that nobody had walked yet. The defense is the same too — know what you’re running, keep it current, and understand what each account and each connection can actually reach.
That mapping is exactly what our environment review delivers. We inventory the third-party software and integrations your business depends on, find the ones that are out of date or forgotten, and trace what each account and connection can reach — so you know where your chains are before someone with better tools than last year’s finds them for you. OpenAI had a bug bounty program and a 14-hour patch turnaround, and this still got as far as it did. The question worth answering isn’t whether you’d be a harder target than they were. It’s whether anyone has ever actually looked.
Sources: Original reporting by The Wall Street Journal; Cybernews; TechRadar Pro; The Tech Portal; and additional coverage, September 2026, together with the researchers’ own public statements. The work was conducted under OpenAI’s official bug bounty program, reported through a bug bounty platform on July 25, 2026, remediated by OpenAI within approximately 14 hours, and awarded a $6,500 bounty. Specific vulnerability details, software versions, and exploitation techniques are summarized here at an awareness level and are available in the researchers’ published write-up for technical readers. Claims about model capability reflect the researchers’ own account of their experience.